| layout | splash | |||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| header |
|
|||||||||||||||||||||||||||||||||||||||||||||
| excerpt | Get the latest **FREE** Enterprise Security Content Update (ESCU) App with **675** detections for Splunk. | |||||||||||||||||||||||||||||||||||||||||||||
| feature_row |
|
{% include feature_row %}
This project gives you access to our repository of Analytic Stories that are security guides which provide background on TTPs, mapped to the MITRE framework, the Lockheed Martin Kill Chain, and CIS controls. They include Splunk searches, machine-learning algorithms, and Splunk Phantom playbooks (where available)—all designed to work together to detect, investigate, and respond to threats.
Try in Splunk Security Cloud{: .btn .btn--success}
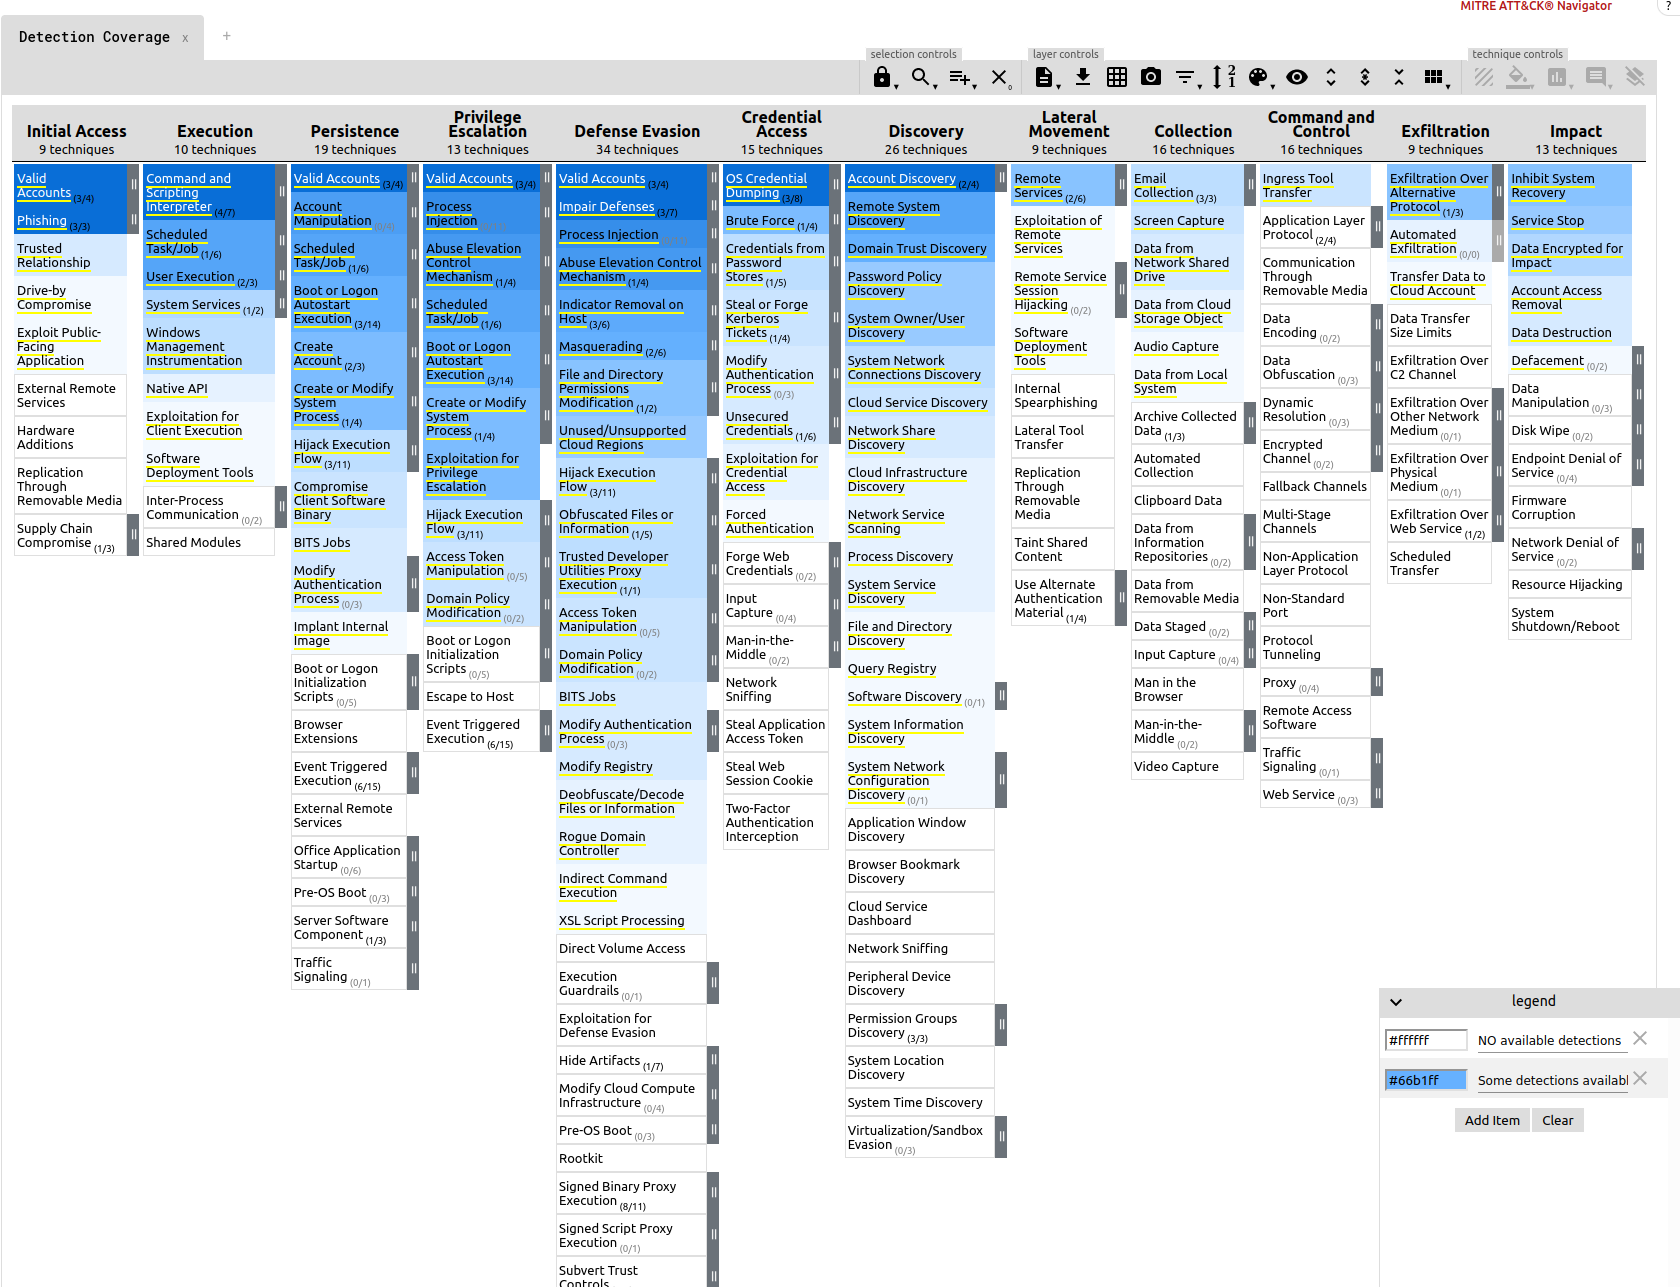
Below is a snapshot in time of what technique we currently have some detection coverage for. The darker the shade of blue the more detections we have for this particular technique.
If you prefer working with the command line, check out our API:
curl -s https://content.splunkresearch.com | jq
{
  "hello": "welcome to Splunks Research security content api"
}
Replay any detection dataset to a Splunk Enterprise Server by using our replay.py tool or the UI. Alternatively use:

The Splunk Attack Range which allows you to create a isolated environment to launch attacks and test/build detections.
Please use the GitHub issue tracker to submit bugs or request features.
If you have questions or need support, you can:
- Join the #security-research room in the Splunk Slack channel
- Post a question to Splunk Answers
- If you are a Splunk Enterprise customer with a valid support entitlement contract and have a Splunk-related question, you can also open a support case on the https://www.splunk.com/ support portal
If you want to help the rest of the security community by sharing your own detections, see our contributor guide for more information on how to get involved!